AcuityAI secures your sensitive commercial data through enterprise-grade controls and industry-leading privacy practices.
SOC 2 Type II Certified and NIST AI RMF Aligned
AcuityAI is SOC 2 Type II certified, which means an independent auditor tested our controls over a multi-month period and confirmed they operated as designed. It's also aligned to the NIST AI Risk Management Framework, which means every AI feature is documented before it ships, tested before deployment, and monitored while it runs.
Protect your data: Enterprise-grade data protection
AcuityAI protects your business data with layered security controls designed to keep information isolated, encrypted, and under your ownership.
Data isolation
Your data is logically isolated and access-controlled within AcuityMD's multi-tenant architecture, with no cross-customer access at any layer.
Encryption by default
Data is encrypted both in transit using TLS 1.2+ and at rest using AES-256 encryption.
You retain ownership
You retain full ownership of your data. AcuityAI acts as a processor, and data can be deleted in accordance with your agreement.
Maintain privacy: Privacy guardrails to protect your data
AcuityAI is designed so you can take advantage of leading AI models without exposing your proprietary data or using it to train third-party models.
No model training
Your inputs are never used to train third-party AI models, and AI vendors cannot train on your data.
Only what's needed
Each request sends the model only what it needs for that task. The model keeps nothing after it responds.
Your activity stays private
Your searches and AI activity are never exposed to other customers. Every third party that processes data on our behalf is security-assessed before onboarding and reviewed on a schedule.
Control access and governance: Security controls that follow your business
AcuityAI carries AcuityMD's existing permissions and security controls into every AI interaction, so users only see and act on the data they're authorized to access.
Permissions carry into AI
Role-based access controls govern data access, and AcuityAI responses respect the same permission boundaries already established in AcuityMD.
No unauthorized access
Your data stays limited to the people authorized to see it. AcuityAI respects your existing permissions and access controls, with least-privilege principles enforced throughout the platform.
You stay in control of AcuityAI actions
AcuityAI can surface recommendations and next steps, but it never acts on your behalf. You decide what to act on, and every action remains under your control.
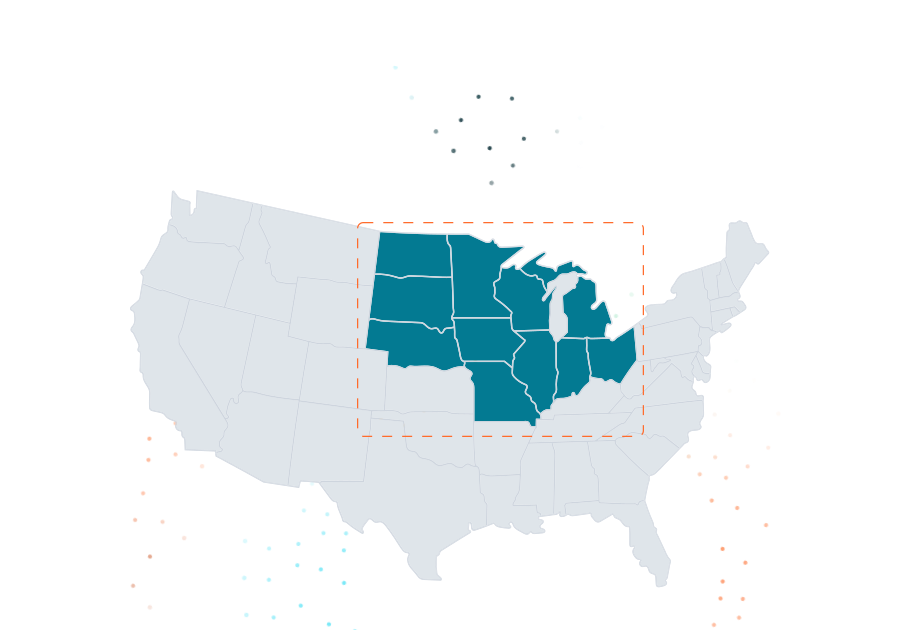
Role permissions: Users only see the territory, region, and quotas relevant to them
Security FAQs
Which AI models does AcuityAI use, and where does our data go?
AcuityAI is vendor-agnostic, so we adopt best-in-class models rather than locking to one provider. Whichever model runs a request, that vendor is contractually prohibited from training on your inputs and is configured for zero data retention where available. Only the data a task requires is sent to the model.
Who can see our data or our AI activity?
Access to customer data is governed by role-based access control under least-privilege principles, with centralized logging, monitoring, and audit trails. Your search and AI activity is never exposed to other customers, and no third party receives raw or identifiable data.
Where does AcuityAI get its information?
AcuityAI works from three sources: AcuityMD's proprietary MedTech dataset, public web sources, and the context your team adds inside the platform. It does not pull from other customers' data, and it has no access to anything outside what your own permissions allow.
How long do you keep our AI activity, and can we delete it?
You retain full ownership of your data, and AcuityAI acts as a processor rather than an owner. Data is retained according to your contractual agreement, and you can request deletion at any time. Deletion follows a documented process that removes data from active systems and propagates through backups on our retention schedule.
Does AcuityAI process patient data?
No. AcuityMD's core dataset covers provider and facility-level activity, not individually identifiable patient information, so AcuityAI does not process PHI in the standard product.